
Current threat surface
CyberSecure Canada Level 2 certified
CSE: QSE
Quantum resilience infrastructure for the AI era.
QSE protects identities, data, systems and critical infrastructure against tomorrow’s threats — today. One platform. Sovereign by design. Trusted by governments, regulators and the operators of national consequence.
Aligned with NIST FIPS 203 · 204 · 205 and CNSA 2.0
- Active users
- 100,000+
- Across diverse global markets
- Enterprise customers
- 200+
- Established market demand and integration
- Commercial partners
- 11
- Strategic alliances expanding reach
- Global deployments
- 10+ countries
- Asia, Europe, North America, South America
Aligned with the institutions shaping the post-quantum standard
- NIST PQC
- FIPS 203 · ML-KEM
- FIPS 204 · ML-DSA
- FIPS 205 · SLH-DSA
- CNSA 2.0
- ETSI QSC
- IEC 62443
- NATO CCEB
Why now
Harvest now, decrypt later is already running.
Adversaries are collecting encrypted traffic today to decrypt it once cryptographically relevant quantum computers arrive. Resilience is no longer a 2030 problem.
Exposure calculator
Is your data already exposed?
Mosca’s inequality: if the years your data must stay secret (X) plus the years your migration takes (Y) exceed the years until a cryptographically relevant quantum computer (Z), data you encrypt today will be readable while it still matters.
- Migration (Y)
- Data shelf life (X)
- Exposure window
Migrate
Data must stay secret
Q-day
Today+17 yrs
5 years exposed
Data you encrypt today would still be sensitive for 5 years after Q-day.
QSE future state
Continuous quantum resilience.
The QSE platform
One platform. Five stages of resilience.
The QSE Quantum Resilience Platform connects every layer of your security posture — from assessment through continuous operation.
Stage 01 · Assess
Cryptographic Posture Score
Cryptographic inventory, risk discovery and regulatory readiness mapped to your estate.
- Crypto discovery
- Risk scoring
- Compliance mapping
Stage 02 · Protect
QAuth & Encryption
Quantum-safe identity, encryption and sovereign key management — workforce and machine.
- QAuth identity
- PQC encryption
- Key lifecycle
Stage 03 · Store
Sovereign Data Layer
Immutable, jurisdiction-aware backup and storage designed for post-quantum durability.
- Resilient storage
- Sovereign backup
- Data residency
Stage 04 · Integrate
APIs & SDKs
Developer-first surfaces — embed resilience into existing systems without re-architecting.
- REST + gRPC
- Language SDKs
- qREK Bridge
Stage 05 · Operate
Entropy & Hardware
True quantum random number generation, HSM integration and continuous health telemetry.
- QRNG entropy
- HSM integration
- Live telemetry
Product ecosystem
Composable. Sovereign. Production-grade.
Start with visibility, then protect, store and operate — each product stands alone and gets stronger together.
Assessment
QPrime
The AI-powered intelligence layer that discovers cryptographic assets, quantifies quantum risk and prioritises your PQC migration — the foundational first step toward crypto-agility.
CISOs · GRC · Security architects
Explore QPrimeDiscovery
QScope
QSE’s CBOM compiler. It automatically finds and organises the encryption across your systems — where it lives, which algorithms, certificates and libraries are in place, and what needs upgrading as standards change.
CISOs · GRC · Security architects · Enterprise IT
Explore QScopeCloud access security
QAuth
A full-strength cloud access security broker (CASB) and integrated SSO platform that secures cloud-centric organisations across their SaaS applications, data and users.
CISOs · IT & SecOps · Cloud admins
Explore QAuthData
QSE Storage
End-to-end quantum-secure, decentralised storage powered by hardware Quantum Random Number Generators. Deploy as managed cloud, air-gapped on-premise, or sovereign hybrid — one QRNG-driven encryption core.
Developers · CISOs · CIOs
Explore QSE StorageSovereign coverage
Built for industries where failure is not an option.
QSE deploys alongside the institutions that hold the world’s most consequential data — and the operators whose uptime defines national resilience.
Technology moat
Capability built over a decade — leveraged through software.
Built for the post-quantum era, not patched for it. QSE’s architecture is designed from the ground up to withstand both classical and quantum attacks.
Proprietary quantum entropy
True randomness, not simulated security. QSE delivers quantum-grade entropy from proprietary, NIST-compliant systems — eliminating predictable key generation. With Entropy-as-a-Service, developers draw it straight from specialised hardware over standard REST APIs.
API-first architecture
Every QSE capability ships as a stable, versioned API surface — adopted across systems, SaaS products and workflows without disrupting operations.
Hybrid & sovereign deployment
On-prem, air-gapped, hybrid or sovereign cloud — the same control plane everywhere.
Hardware integration
Native fabric across HSMs, secure elements and edge silicon.
Decentralised by design
No single point of failure, no centralised trust risk. Data stays secure, available and tamper-resistant under advanced threat models.
Certified & compliant
Independently audited. Standards-aligned.
Designed for regulated industries and critical data — governments, financial institutions, healthcare and data-sensitive enterprises.
CSCCL2
Certified
CyberSecure Canada — Level 2
Meets the federal CyberSecure Canada baseline (CAN/DGSI 104:2021, Rev 1: 2024) — an independently audited standard for cyber hygiene, incident response and secure development.
AICPASOC 2
Compliant
SOC 2
Security, availability and confidentiality controls aligned with the AICPA Trust Services Criteria for handling customer data.
NISTPQC
Aligned
NIST post-quantum cryptography
Implementations align with FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA) for standards-based key exchange and signatures.
USHIPAA
Compliant
HIPAA
Supports HIPAA-compliant deployments with the administrative, physical and technical safeguards required to protect ePHI.
Leadership
Building tomorrow with proven leadership.
Cryptographers, intelligence-community veterans and infrastructure operators — shipping post-quantum systems that hold up under audit and adversary.
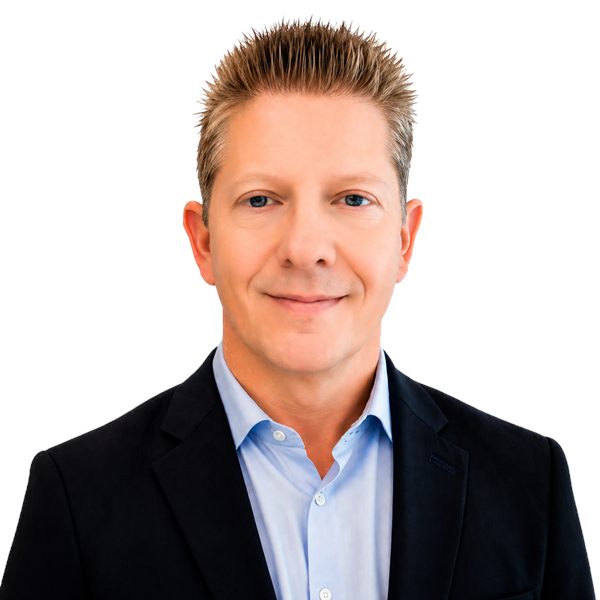
Chief Executive Officer
Ted Carefoot
20+ years leading product, software and cloud initiatives across AI-driven cloud, digital security and immersive technologies.
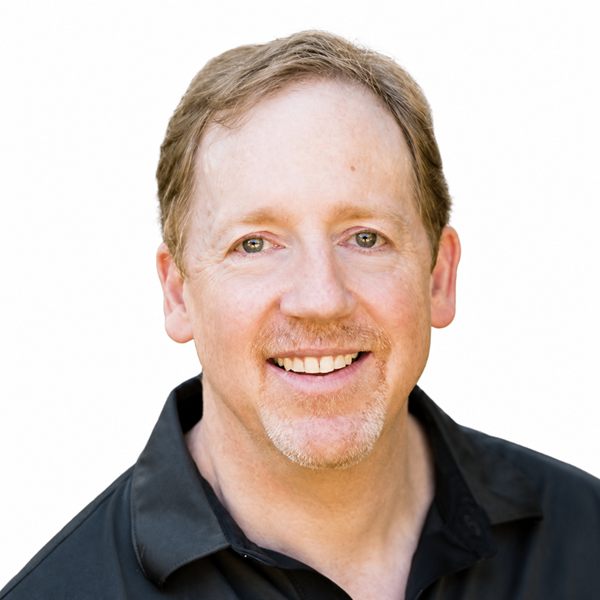
Chief Technology Officer
Mike Massing
Cybersecurity and AI veteran with 30+ years across cryptography, secure data management, blockchain and network architecture.
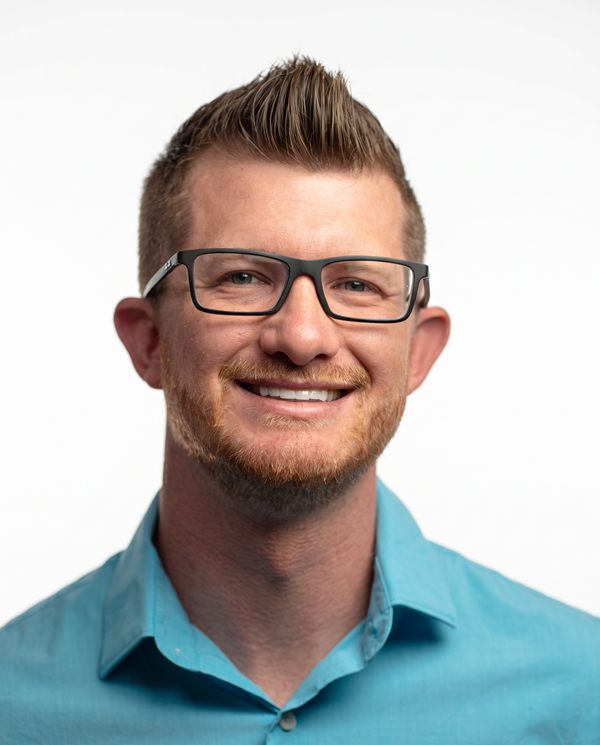
Chief Intelligence Officer
Joseph Hall
Recognised security leader with experience across Dell, Fortinet, Sophos, Symantec and Infoblox.
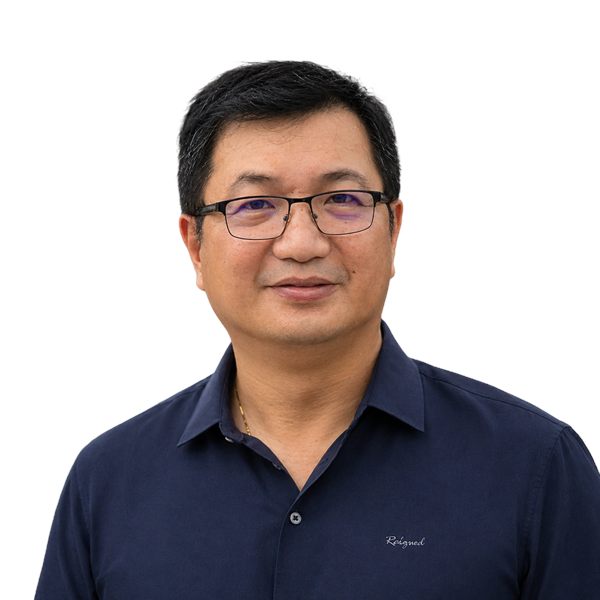
Head of Sales & Finance Strategy
Eugene Suarez
Leads revenue strategy, aligning enterprise sales motion with capital planning for sovereign post-quantum deployments.
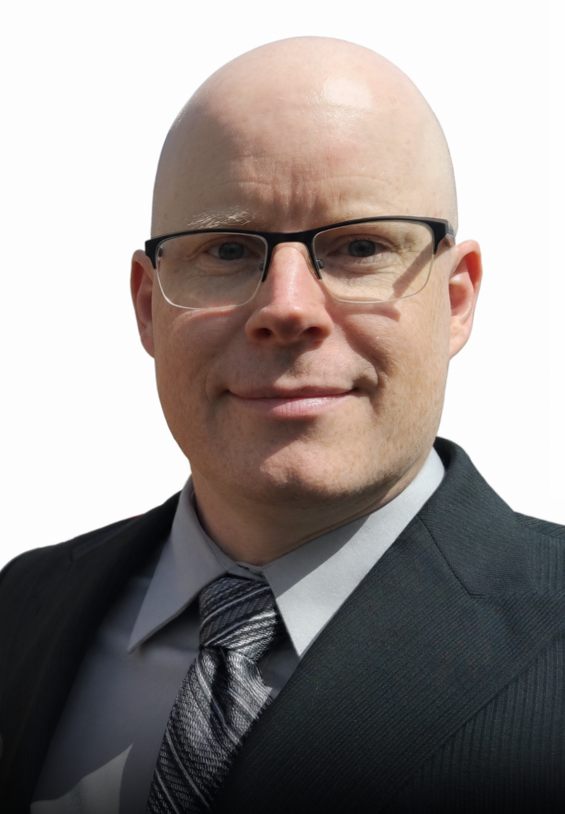
Vice President of Product
Andrew Knight
Two decades of software development and product leadership across England, Australia and Canada.
Thought leadership
Research from QSE Labs.
Research
The crypto-agility imperative
Leading institutions are operationalising NIST FIPS 203 in production estates.
BriefCNSA 2.0 readiness, 2026
Changes are coming for federal vendors and defence primes — including their tier-one suppliers.
WhitepaperEntropy as infrastructure
Why true QRNG matters when AI-grade attackers join the threat model.
Newsroom
Latest from QSE.
- InvestorsQSE to Host Investor Webinar on October 22, 2026
- CorporateQSE Issues CEO Letter to Shareholders Highlighting Commercial Execution and Growth Priorities
- LeadershipQSE Appoints Threat Intelligence Veteran Joseph Hall as Chief Intelligence Officer
- PartnershipsQSE Advances European Space Security Strategy Through European Space Agency Engagement
Investors · CSE: QSE
A category-defining position in post-quantum infrastructure.
QSE operates with the leverage of a software company against an infrastructure market: high-IP, automation-driven, with regulatory tailwinds and a multi-year head start in entropy and key management.
- High-IPSoftware leverage against an infrastructure market
- TailwindsPQC mandates landing across sectors and jurisdictions
- $6MPrivate placement closed
Get started now
Find out how quantum-ready you are.
A QSE specialist will guide you through:
- The 12-point Quantum Readiness assessment, step by step
- Mapping to NIST FIPS 203/204/205 and the mandates landing in your sector
- Your personalised report and migration roadmap